Identity & Network Trust
V2 console
This card lives in Policy Engine > LLM Gateway at web.quilr.ai/policy. Edits join the shared draft and take effect once you review and publish a revision.
Require callers to prove who they are, require a conversation ID, and limit where requests may come from. Runs at the request stage.
Sections
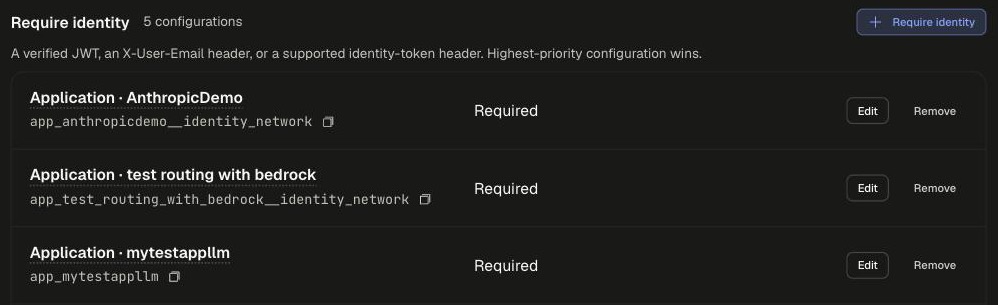
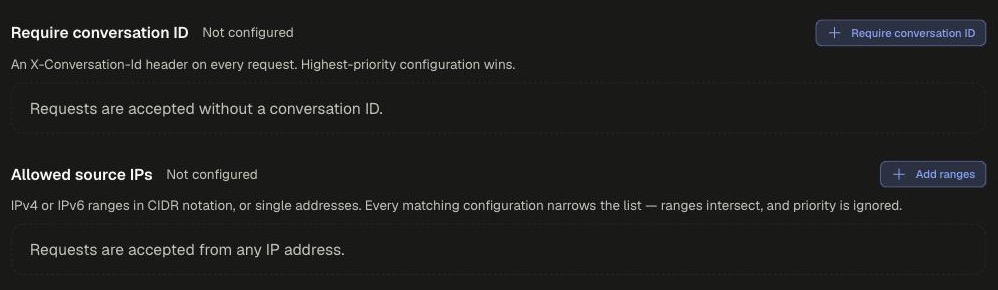
The card always shows the same three controls.
Settings
Every add button opens one dialog with all three requirements. The button you clicked pre-selects its own row.
Set at least one requirement. The policy name is generated from the scope.
Example
govern_production_identity_networkrequest
runs on requestpriority 850
WhenRequest metadata . environmentisproduction
Then
Require identitytrue
Require conversation IDtrue
Allowed source IP ranges10.0.0.0/82001:db8:1200::/48
Scoping and precedence
- Applies to: Everyone, People, Smart group, Application, App tag, API surface, Environment, Prompt text, Tool, Source network, or Except.... Requested model and Provider are not offered.
- Require identity and Require conversation ID: the highest-priority matching configuration wins.
- Allowed source IPs ignore priority. Every matching configuration narrows the list: ranges intersect, the narrower of two overlapping ranges is kept, and ranges that do not overlap are dropped. If nothing survives, every matching request is denied.
Check overlapping IP lists
Two configurations with disjoint ranges (for example one app's office range and a tenant-wide VPN range) leave no allowed address, so the matching traffic is blocked.
Legacy app settings
- Source IP lists replace Source IP restrictions in Security Guardrails.
- Require identity overlaps with Enforce Identity in the app's Identity Aware settings. How identity is verified (headers, JWT, JWKS) is still configured per app there.